Cookies Privacy
I accept Cookies Policy We use cookies to understand how you use our website and to improve your experience. By continuing to use this website, you accept our Link is copied!

Social-Engineering Testing

Social-engineering testing evaluates whether attackers could influence employees, help desks, suppliers or physical controls to disclose information, approve actions or grant access. The service is for organisations that need controlled evidence of human and process vulnerabilities, not merely completion statistics from awareness training.

What this service helps you achieve?

The purpose is to validate realistic attack paths safely and convert technical weaknesses into remediation priorities.

  • Identify behaviours and process weaknesses that enable manipulation.
  • Test escalation, verification and reporting procedures.
  • Measure risk by scenario, role and organisational unit.
  • Provide evidence for targeted awareness and control improvements.
  • Validate whether previous training changes real behaviour.

Scope: What we examine?

Scope is fixed with you before any work starts. Depending on the objective, environment and authorised access, the engagement may cover:

  • Email phishing and targeted spear-phishing scenarios.
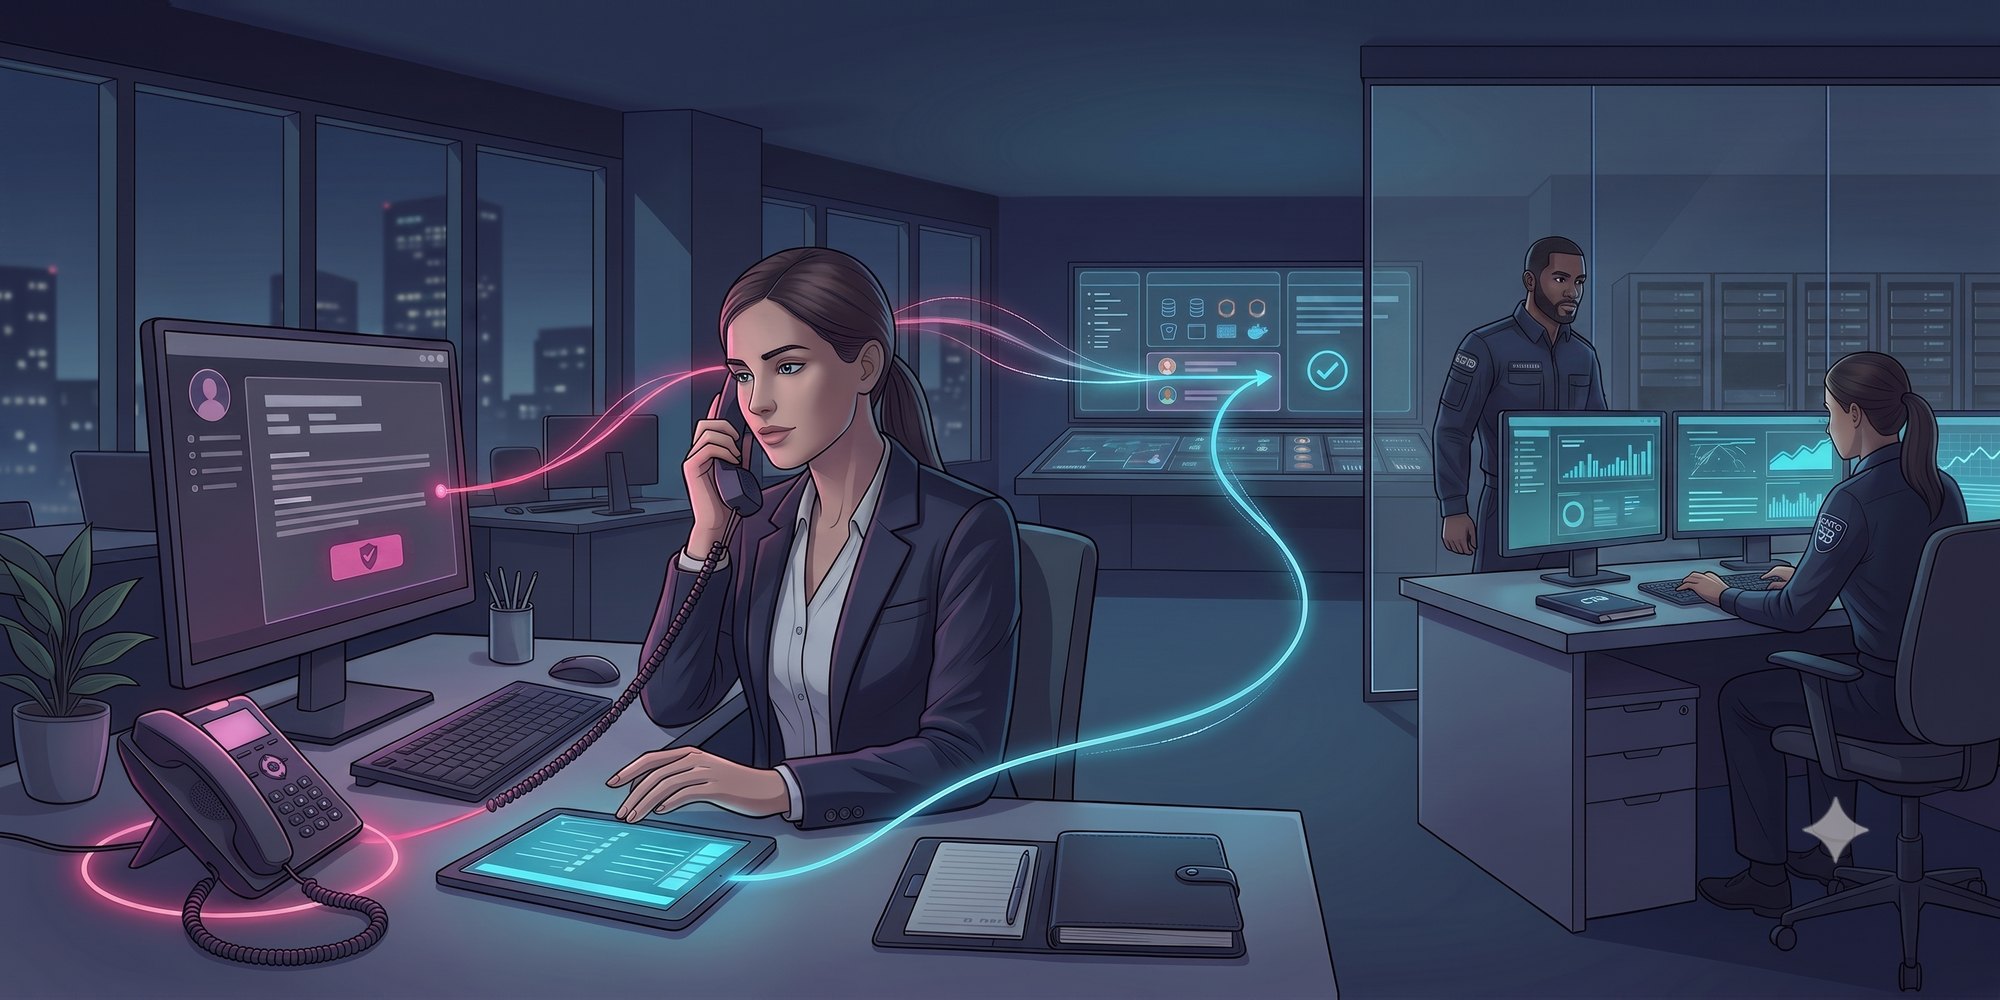
  • Telephone vishing and help-desk verification tests.
  • SMS or collaboration-platform scenarios where approved.
  • Physical entry, tailgating or pretexting where expressly authorised.
  • Credential, payment, data-disclosure and access-request scenarios.
  • Employee reporting and escalation behaviour.
  • Privacy-conscious metrics and safe data handling.
  • Post-exercise coaching and lessons learned.

Our approach, step by step

Agree target groups, excluded individuals, data collection, safe payloads, stop conditions and communications.

1. Set ethical and legal boundaries:

Create pretexts and scenarios relevant to the organisation’s roles, suppliers and business processes.

2. Design realistic scenarios:

Use controlled infrastructure and prevent unnecessary collection of sensitive information.

3. Run the exercise safely:

Measure action, reporting, verification and escalation rather than relying on click rate alone.

4. Analyse behaviour and process:

Provide targeted recommendations, coaching and retest options.

5. Debrief and improve:

Deliverables you can act on

Everything we hand over speaks to both leadership and the people who will act on it. Depending on scope, they may include:

  • Scenario plan and authorisation record.
  • Results by scenario, role and organisational unit.
  • Process-control and verification observations.
  • Privacy-aware metrics and limitations.
  • Targeted remediation and awareness recommendations.
  • Management summary.
  • Retest or follow-up campaign plan.

How we from Cyber Tech Group keep the work focused?

Testing is governed by written authorisation, explicit exclusions, safety limits and emergency contacts. Material findings are manually validated, supported with reproducible evidence and explained in terms of realistic impact rather than scanner severity alone.

When this service is the right choice?

  • Phishing and fraud risk remains high despite training.
  • Help-desk or payment verification processes need testing.
  • A major awareness programme requires a behavioural baseline.
  • The organisation has experienced Business Email Compromise (BEC) or impersonation attempts.
  • Physical-access procedures need validation.
  • Management needs evidence of reporting and escalation behaviour.

How we work: standards and boundaries?

The engagement may draw on NIST security-awareness guidance, recognised social-engineering testing ethics, applicable privacy and employment requirements. Referencing a framework describes how we structure the work; it is not, in itself, a certification, accreditation or regulatory ruling.


Timelines are set once scope is agreed, and vary with the size of the environment and the availability of evidence and stakeholders.


Testing must be proportionate, authorised and privacy-conscious. It should not humiliate employees, collect unnecessary credentials or create unsafe operational consequences. Routine training simulations and adversarial social-engineering assessments must remain clearly distinguished.
Discuss Social-Engineering Testing with us. A short scoping session confirms the objective, boundaries, evidence, delivery model and outputs before we issue a proposal.

Related services

Frequently asked questions

What does Social-Engineering Testing cover?

Scope is fixed with you before any work starts. Typical areas include email phishing and targeted spear-phishing scenarios, Telephone vishing and help-desk verification tests, SMS or collaboration-platform scenarios where approved, and Physical entry, tailgating or pretexting where expressly authorised. Exclusions, required access, your responsibilities and acceptance criteria are all set out in the proposal and SoW.

What will we receive at the end of the engagement?

Deliverables depend on the agreed objective and may include scenario plan and authorisation record, Results by scenario, role and organisational unit, Process-control and verification observations, and Privacy-aware metrics and limitations. Every significant finding is tied to evidence, business impact, priority and a clear owner for the next step.

Could testing disrupt production systems?

Authorised testing can create risk if it is poorly controlled. Cyber Tech Group agrees testing windows, prohibited techniques, stop conditions and emergency contacts before work begins, and uses higher-risk techniques only with explicit approval.

Is remediation retesting included?

Retesting can be included in the initial scope or ordered after remediation. It validates the previously confirmed findings and closely related bypass conditions; it is not automatically a complete new assessment.

How long does the engagement take?

Timelines are set once scope is agreed, and vary with the size of the environment and the availability of evidence and stakeholders.

How does this relate to Phishing Simulations?

These services answer related but distinct questions. Scoping identifies whether Social-Engineering Testing, Phishing Simulations, or a coordinated programme is the smallest useful approach without duplicating work.

What are the principal limitations?

Testing must be proportionate, authorised and privacy-conscious. It should not humiliate employees, collect unnecessary credentials or create unsafe operational consequences. Routine training simulations and adversarial social-engineering assessments must remain clearly distinguished.