Cookies Privacy
I accept Cookies Policy We use cookies to understand how you use our website and to improve your experience. By continuing to use this website, you accept our Link is copied!

Cloud Penetration Testing

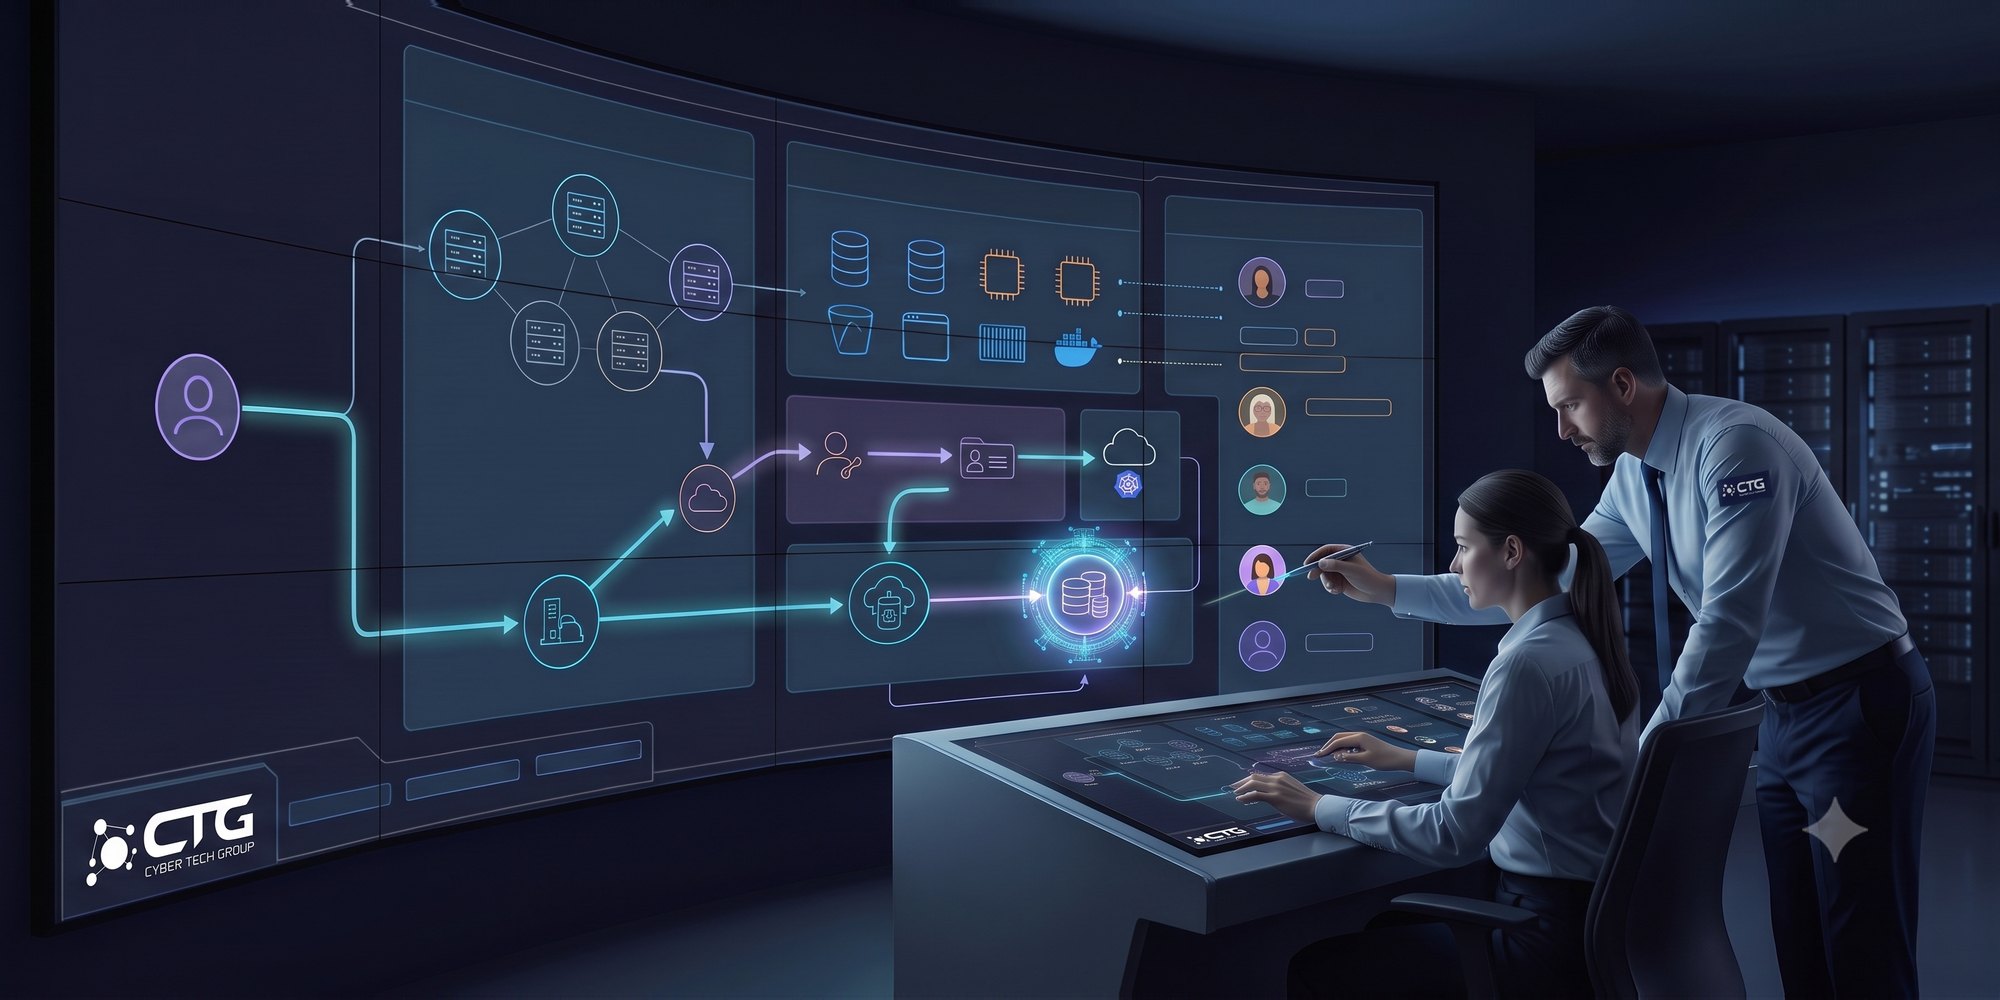
Cloud penetration testing simulates authorised attacker behaviour against cloud-hosted workloads, identities and control planes to validate exploitable risk. It is designed for organisations that need adversarial testing beyond configuration review, particularly after major cloud changes or before high-impact services go live.

What you gain from this engagement?

The purpose is to validate realistic attack paths safely and convert technical weaknesses into remediation priorities.

  • Demonstrate how cloud identities and services could be abused.
  • Validate paths from exposed workloads to sensitive cloud resources.
  • Test privilege escalation, lateral movement and trust relationships.
  • Assess whether monitoring detects the tested behaviours.
  • Prioritise remediation by realistic cloud impact.

Assessment scope and outputs

The exact boundaries are settled before the engagement begins. Depending on the objective, environment and authorised access, the engagement may cover:

  • Authorised AWS, Microsoft Azure or Google Cloud projects and subscriptions.
  • Cloud identities, roles, policies and trust relationships.
  • Public endpoints, compute, storage, databases and serverless services.
  • Metadata services, secrets and temporary credentials.
  • Network controls, peering and hybrid connectivity.
  • Container and orchestration components where included.
  • Privilege escalation and cross-account or cross-subscription paths.
  • Logging and detection observations linked to the test.

How the engagement works?

Review cloud-provider testing rules, tenancy, assets, exclusions and emergency contacts.

1. Confirm provider and customer authorisation:

Identify control-plane relationships, services, workloads and trust paths.
 

2. Map cloud architecture and identities:

Select realistic paths relevant to the customer’s architecture and data.

3. Develop threat-informed scenarios:

Validate vulnerabilities and misconfigurations without exceeding agreed impact limits.

4. Perform controlled testing:

Explain attack chains, evidence, remediation and optional retest results.

5. Report and validate fixes:

Your expected deliverables

Reports serve decision-makers and implementation teams alike. Depending on scope, they may include:

  • Cloud penetration-testing plan and rules of engagement.
  • Attack-path and privilege-escalation findings.
  • Evidence linked to affected cloud resources and identities.
  • Business-impact and blast-radius analysis.
  • Prioritised remediation guidance.
  • Detection observations.
  • Retest report where included.

Governance and quality control

Тesting is governed by written authorisation, explicit exclusions, safety limits and emergency contacts. Material findings are manually validated, supported with reproducible evidence and explained in terms of realistic impact rather than scanner severity alone.

When organisations engage us?

  • Before officialy launching live a critical cloud service.
  • After major identity, network or landing-zone changes.
  • Following cloud posture or architecture findings that require exploit validation.
  • After an account or credential compromise.
  • For customer or regulatory assurance.
  • When hybrid trust and privilege paths are poorly understood.

Standards, timing and service boundaries

The engagement may draw on cloud-provider penetration-testing policies, MITRE ATT&CK for Cloud, OWASP guidance where applications are included, NIST technical guidance. Naming a framework indicates our approach; it does not constitute certification, accreditation or a regulatory decision.


Duration is agreed after scoping and depends on environment size, available evidence and stakeholder availability.


Cloud penetration testing must follow both customer authority and provider rules. It is not the same as a broad cloud posture assessment and does not include denial-of-service, other tenants or unmanaged third-party services unless expressly authorised.
Discuss Cloud Penetration Testing with us. We start with a scoping conversation to fix the objective, limits, evidence, delivery model and deliverables ahead of any proposal.

Related services

Frequently asked questions

What does Cloud Penetration Testing cover?

The exact boundaries are settled before the engagement begins. Typical areas include authorised AWS, Microsoft Azure or Google Cloud projects and subscriptions, Cloud identities, roles, policies and trust relationships, Public endpoints, compute, storage, databases and serverless services, and Metadata services, secrets and temporary credentials. Scope limits, access needs, client responsibilities and acceptance criteria are captured in the proposal and SoW.

What will we receive at the end of the engagement?

Deliverables depend on the agreed objective and may include cloud penetration-testing plan and rules of engagement, Attack-path and privilege-escalation findings, Evidence linked to affected cloud resources and identities, and Business-impact and blast-radius analysis. Findings are traceable to evidence, impact, priority and the person responsible for acting.

Could testing disrupt production systems?

Authorised testing can create risk if it is poorly controlled. Cyber Tech Group agrees testing windows, prohibited techniques, stop conditions and emergency contacts before work begins, and uses higher-risk techniques only with explicit approval.

Is remediation retesting included?

Retesting can be included in the initial scope or ordered after remediation. It validates the previously confirmed findings and closely related bypass conditions; it is not automatically a complete new assessment.

How long does the engagement take?

Duration is agreed after scoping and depends on environment size, available evidence and stakeholder availability.

What are the principal limitations?

Cloud penetration testing must follow both customer authority and provider rules. It is not the same as a broad cloud posture assessment and does not include denial-of-service, other tenants or unmanaged third-party services unless expressly authorised.